Securing Arm Servers
summary
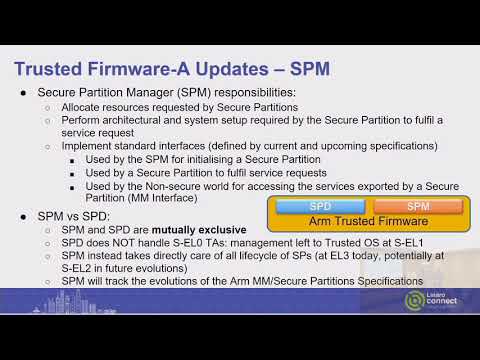
Open-source Secure Boot and secure variable access land in Trusted Firmware and UEFI EDK2 with upstream patches and a new standalone MM package; code targets the Arm System Guidance SGI 575 and is slated for the feature-105 release. Implementation uses a Secure Partition Manager (SPM) to instantiate a single secure partition that services get/set variable calls via MM communicators and a NOR SPI flash driver; runtime relies on software crypto (no hw crypto) and boots Fedora/Debian on SGI 575. Sources and patches are linked in the resources and examples.
AI-written summary · about
chapters (9)
- 0:00Introduction to securing Arm servers
- 1:05Secure partitions concept and architecture
- 8:41Changes in Trusted Firmware
- 10:51Standalone MM changes
- 12:44Arm System Guidance platforms
- 14:31SGI 575 platform overview
- 17:04Secure partition access example
- 20:39Future evolution of the framework
- 23:10Q&A and resources
related talks
 22mBoot Requirements and Strategies for the Edge
 39mTrusted Firmware M, Secure Partitioning – Compartmentalization in IoT
 38mUEFI Secure Boot in U-Boot
 39mSecuring firmware: Secure and Trusted boot in OpenBMC
 42mwolfBoot: Open Source Secure Boot and Remote Firmware Updates in Safety-critical..
 39mTrusted Firmware M, Secure Partitioning – Compartmentalization in IoT
 26mKeynote: Trusted Firmware – Build Security Collaboratively
 23mTrusted Firmware M – what’s cooking?