DOM XSS Protection at Scale

summary
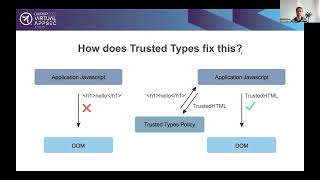
Claims that Trusted Types plus a rollout pipeline eliminates DOM XSS at scale, with Google reporting zero DOM XSS across hundreds of apps serving billions of users. Practical tools are CSP with required-trusted-types-for, runtime trusted types policies, a safe-values library and t-c static checks. Built pieces include reporting endpoints, DevTools violation tracing, legacy/reviewed conversions, default-policy fallbacks and occasional forked patches for dependencies; enforcement mode blocks bad assignments and reporting mode lets teams triage before switching to enforcement.
AI-written summary · about
chapters (9)
- 0:00Introduction
- 1:48DOM XSS critical issue
- 4:16DOM-based XSS vulnerabilities
- 8:08Trusted Types mitigate DOM XSS
- 11:41Building Trusted Types apps
- 15:11Refactoring apps for Trusted Types
- 21:26Debugging Trusted Types violations
- 27:48Third-party dependencies in Trusted Types
- 32:26Key takeaways
related talks
 36mSecuring the DOM from the Bottom Up
 57mTrusted Types: A World Without XSS
 31mSecuring the DOM from the Bottom Up
 16mEliminating XSS Angular applications by adopting TT
 31mAchieving Secure Software through Redesign
 27mSecuring Angular with Trusted Types
 01h 01mClient-Side Protection Against DOM-Based XSS Done Right (tm)
 40mClient-Side Protection Against DOM-Base...