Eliminating XSS Angular applications by adopting TT

summary
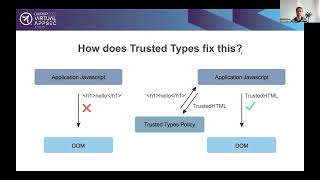
Explains a concrete rollout: enable Trusted Types via CSP and add to angular.json, detect violations with ng serve, ng e2e and the static analyzer TSAC, fix by swapping injection sinks for safe DOM APIs or by writing a policy that uses DOMPurify, then switch from report-only to enforcement. Claims a measurable impact—about 61% of past DOM XSS reports would be mitigated—and shows an Angular vulnerability that enforcement actually blocks.
AI-written summary · about
chapters (10)
- 0:00Intro
- 0:40Google's VRP in 2018
- 2:34Content Security Policies (CSP)
- 6:17Identifying violations
- 7:20Fixing violations
- 10:19Preventing regressions
- 11:13Restricting policy creation
- 12:10Angular policies
- 13:14Deploying Trusted Types
- 14:25Benefits
related talks
 27mSecuring Angular with Trusted Types
 57mTrusted Types: A World Without XSS
 31mBoosting the security of your Angular 2 application
 25mSecuring Angular with Trusted Types
 34mDOM XSS Protection at Scale
 32mAngular and the OWASP top 10
 48mSecurity Risk: Single-Page Applications.
 31mAngular and the OWASP top 10