Securing Angular with Trusted Types

summary
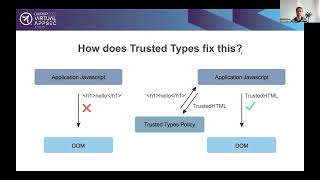
Claims that enabling require-trusted-types-for 'script' plus allowing Angular’s built-in policy prevents DOM-based XSS by making innerHTML accept only TrustedHTML objects, and that Google observed no DOM XSS after adoption. Shows how Angular sanitizer auto-creates TrustedHTML, and how risky calls like bypassSecurityTrustHtml, direct innerHTML via ViewChild/ElementRef or Renderer2 bypass protections. Recommends enabling Trusted Types in development, vetting each of the ~15 errors it may reveal, and using a default policy with DOMPurify or polyfills for non‑Chromium browsers.
AI-written summary · about
chapters (9)
- 0:00Intro
- 4:17Angular
- 8:39Bypass Security
- 14:03Trusted Types
- 14:18Danger
- 14:55Unsafe Bypass
- 15:36Browser Support
- 18:14Takeaway
- 21:55Summary
related talks
 27mSecuring Angular with Trusted Types
 57mTrusted Types: A World Without XSS
 36mSecuring the DOM from the Bottom Up
 16mEliminating XSS Angular applications by adopting TT
 31mSecuring the DOM from the Bottom Up
 17mThere's Safety in Angular
 24mSecurity in Angular 2
 31mBoosting the security of your Angular 2 application