Securing the DOM from the Bottom Up

summary
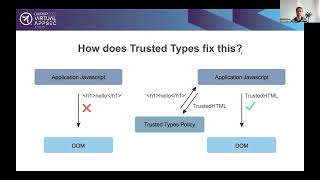
Google’s solution is trusted types, a browser API that replaces dangerous DOM strings with objects like trusted HTML and three others, enforced via a Content-Security-Policy directive and per-site policies. It ships behind an origin trial in Chromium, has a 66-byte minimal polyfill and larger framework patches (Angular example), and already reduces DOM‑XSS exposure by orders of magnitude in pilots. Policies and a default policy make legacy code report or fail, and lint/compile checks prevent unsafe string-to-sink assignments.
AI-written summary · about
chapters (6)
- 0:00Start
- 1:19Google Vulnerability Reward Program payouts in 2018
- 6:39The idea behind Trusted Types Strongly typed DOM API
- 11:41Creating Trusted Types 1. Create policies with validation rules
- 13:50Control over policies Control policy creation
- 28:15Project status • Active development.looking for your feedback
related talks
 36mSecuring the DOM from the Bottom Up
 27mSecuring Angular with Trusted Types
 57mTrusted Types: A World Without XSS
 34mDOM XSS Protection at Scale
 25mSecuring Angular with Trusted Types
 59mThe Final Frontier: Security APIs in Modern Browsers
 19mWeb Platform Security
 41mSecuring Web Apps with Modern Platform Features