A Log-Structured Merge Tree-aware Message Authentication Scheme for Persistent...
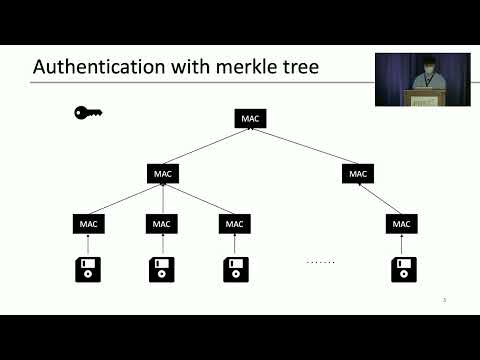
summary
TWEEZER extends RocksDB and implements per-SST authentication keys plus a hash chain to avoid slow hardware counters, reproduces Speicher for comparison, and measures with db_bench. Claim: fine-grained per-SST MACs cut SGX cryptographic overhead and protected-memory use. Build works: TWEEZER runs on SGX, outperforms reproduced Speicher by 1.94–6.23×, and reduces confidential-computing slowdown from ~16–30× down to ~4–9×. Tradeoffs: higher storage overhead and worse long range-scan performance; short reads are much faster.
AI-written summary · about
chapters (11)
- 0:00Intro
- 0:41KVSs need to run in an enclave
- 2:16Existing system: Speicher (FAST '19)
- 4:12Our system: Tweezer
- 5:02Authentication with merkle tree
- 7:16Fine-grained authentication
- 8:48Evaluation
- 9:16Tweezer outperforms Speicher
- 10:05Tweezer leverage trusted memory efficiently
- 11:05Drawbacks of tweezer Range Query 12
- 12:31Conclusion
related talks
 21mSPEICHER: Securing LSM-based Key-Value Stores using Shielded Execution
 41mTPMs, Merkle Trees and TEEs: Enhancing SLSA with Hardware-Assisted...
 24mSplinterDB: Closing the Bandwidth Gap for NVMe Key-Value Stores
 13mMlsDisk: Trusted Block Storage for TEEs Based on Layered Secure Logging
 50mTrusted Execution Environments Meet the Blockchain
 41mPanel: A New Root Of Trust: Changing Computing With TEE
 18mOn Scalable Integrity Checking for Secure Cloud Disks
 01h 07mEmerging Embdedded Memories and Storage