SPEICHER: Securing LSM-based Key-Value Stores using Shielded Execution

summary
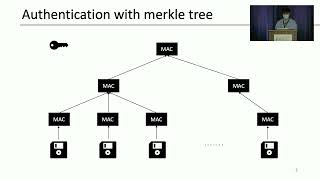
Speicher is a secure LSM-backed key-value store that provides confidentiality, integrity and freshness for persistent data by extending trust beyond the SGX enclave to untrusted storage. It implements an authenticated, confidentiality-preserving LSM, uses asynchronous trusted counters to prevent rollback/forking, and adds a direct-I/O library built on Intel SPDK to eliminate enclave I/O bottlenecks. Speicher is implemented by extending RocksDB, evaluated with RocksDB benchmarks, and shows measured overheads roughly between 15% and 50% while keeping the TCB small.
AI-written summary · about
chapters (8)
- 0:00SPEICHER project intro
- 3:04Security for key-value storage
- 6:28LSM design challenges
- 9:53LSM integrity mechanisms
- 13:14SPEICHER implementation
- 16:04Performance overhead
- 18:18Client-side security
- 20:32Q&A
related talks
 13mA Log-Structured Merge Tree-aware Message Authentication Scheme for Persistent...
 27mSecurity++: Hide Your Secrets via a Distributed Hardware Security Mod...
 18mLITESHIELD: Secure Containers via Lightweight, Composable Userspace μKernel...
 19mCoSMIX: A Compiler-based System for Secure Memory Instrumentation and Execution in Enclaves
 13mMlsDisk: Trusted Block Storage for TEEs Based on Layered Secure Logging
 12mSpanDB: A Fast, Cost-Effective LSM-tree Based KV Store on Hybrid Storage
 06mSGX-SSD: A Policy-based Versioning SSD with Intel SGX
 20mSupporting Confidential Workloads with SPIRE