Frontend Security is a Thing
summary
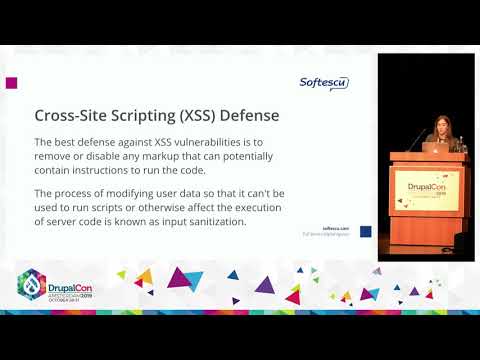
Covers concrete attacks and defenses: OWASP lists SQL injection as the top risk in 2013 and 2017 and shows four SQLi flavors (incorrect escaping, bad typing, blind and second‑order) with escapes and typed checks as fixes; demonstrates how cross-site scripting (reflected and persistent) steals cookies and how Content Security Policy + sanitization stops it; lists CSRF tokens, rename uploads/disable execution, private file uploads, 2FA and password modules, and Drupal tools like Security Review and nikto sukui security headers as practical checks.
AI-written summary · about
chapters (13)
- 0:00Intro
- 0:50Who am I
- 1:12Security and web development
- 2:03Attack on websites
- 4:07Incorrect filtered escape characters
- 5:21Incorrect type handling
- 8:35Reflected
- 10:47Content Security
- 13:29Drupal is Secure
- 15:37Antispam Measures
- 17:11Frontend Security Flaws
- 17:35Never Trust Data
- 17:58Questions
related talks
 37mFront-end Security
 01h 04mWeb Security And You
 30mWeb Security Engineering - Protect all layers of your project
 59mWeb Application Security Trends
 52mDemystifying Front-End Security
 01h 00mWeb Application Security Risks: A Look at OWASP Top Ten 2017
 01h 03mTen Key Steps for Enhanced Web App Security
 48mSecure Development on the Frontend