Leaving No Input Unsanitized
summary
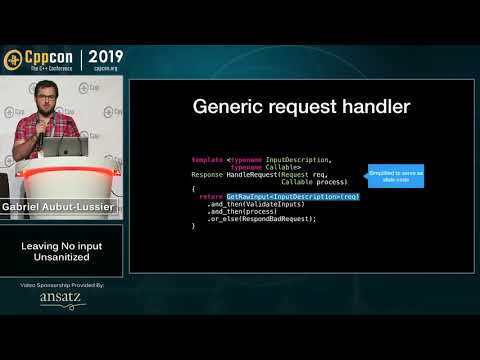
Claims a design that forbids direct access to raw inputs and forces explicit enumeration of every input source and shape, implemented as declarative input descriptions that map headers or body to user types. Provides a generator request handler that extracts raw data, runs per-type validation via a generic validator template returning optionals, and only invokes the business lambda when every input validates. Proof-of-concept runs on HTTP REST requests, works end-to-end, and is claimed easily generalizable to other tainted inputs.
AI-written summary · about
chapters (5)
related talks
 52mTrust No Input: Taint Analysis at Compile Time
 17mModel-Based Input Validation: Preventing Prompt Injection Attacks
 46mSecure Coding Patterns
 25mLittle Bobby Tables: Understanding Data Validation and Sanitization
 52mSecure by Design, Revisited - Insights & Pitfalls
 59mSecure Coding Back to Basics
 01h 00mSecuring React: Prompt Engineering for Robust and Secure Code Generation
 48mEnding Injection Vulnerabilities