V for Vendetta:Dissecting a Global Phishing Platform After Being Phished
summary
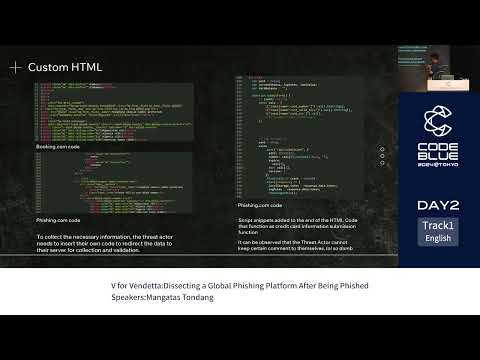
Investigation starts after a booking.com chat link that exposes booking details and leads to five confirmed phishing attempts across four countries; analysis uses urlscan.io and VirusTotal and finds 1,500+ reported phishing URLs reusing site HTML/CSS, Cloudflare/DoS-Guard hosting, and merchant compromises via a Fedar info stealer. Source code snapshot on GitHub reveals an admin panel, Telegram bot, templates and telecopier platform features that run three-stage credit‑card capture with submit.js and blur.input.js and live customer‑support chat.
AI-written summary · about
chapters (8)
- 0:00Phishing investigation introduction
- 3:14Researching the phishing platform
- 6:07Travel booking phishing case
- 12:14Booking.com phishing similarities
- 17:59Travel and e-commerce phishing
- 22:16Telecopier platform source code
- 25:16Telecopier platform operation
- 27:47Preventing phishing recommendations
related talks
 29mHook, Line, and Tinker: A Dive into Phishing Campaign Sites
 27mCatching the Phisherman
 01h 01mSomething Something Cyber
 30mTargeted Web Skimming on E-Commerce Sites
 58mCatching Transparent Phish: Understanding and Detecting MITM Phishing Kits
 54mDark Fairytales From A Phisherman
 56mCybersecurity & Privacy From The Global Lens
 01h 00mHack to the Future