Targeted Web Skimming on E-Commerce Sites

summary
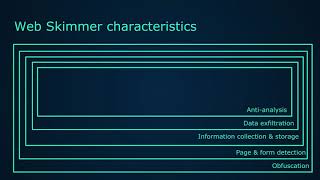
Claim: attackers implant obfuscated JavaScript into vulnerable e‑commerce templates, load a fake Google API domain to harvest form fields, and exfiltrate payment data to attacker servers. Investigators trace reused master scripts, domains googlebapi.com and jqueryapistatic.com, domain registrations (Jul 28 2020, Nov 7 2021), and payloads unpacked with a JavaScript packer; confirmed impact is about ~9,000 card records from roughly 8,000 customers across ~15 targeted sites. Response uses FIRST CTI methodology: code comparison, monitoring, infrastructure coordination, and law‑enforcement sharing.
AI-written summary · about
chapters (10)
- 0:00Introduction and overview
- 1:38Web skimming mechanics
- 5:37Case study investigation
- 8:29Malicious script analysis
- 12:48Threat activity monitoring
- 15:32Threat research findings
- 17:06CTI implementation framework
- 21:03Assessing risk and impact
- 24:12Calculating and managing risk
- 27:27Data processing and wrap-up
related talks
 34mMagecart 2020 The New Face of XSS
 33mWhere's my dough?! A look at web skimming attacks on
 48mRegulation and Risk When Your Customer’s Browser Leaks Data
 44mMagecart - The Rising Threat to e-commerce Websites
 01h 00mApisecure, 14 & 15 March 2023 - Arik Atar, Threat Intelligence Researcher at Human Security.
 40mHow I Hacked Your Website and You Didn’t Even Know
 48mDawn Of The Dead: The Tale Of The Resurrected Domains
 29mYour Scripts In My Page - What Could Possibly Go Wrong?