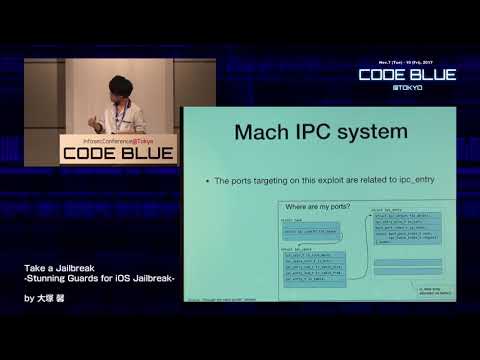
Take a Jailbreak -Stunning Guards for iOS Jailbreak-
summary
Combines three public bugs to move from app to root then to kernel: uses CVE-2016-7637 port uref corruption to man‑in‑the‑middle IPC, runs a 62‑iteration generation bump with ~20 middle ports and ~5000 spray ports to align slots, triggers CVE-2016-7644 set_dp_control_port race to create a dangling ipc_entry, overwrites ip_context/ol_port descriptors to spawn a kernel task port, then bypasses KPP/AMFI/MAC/KASLR by manipulating TTBR1 and page tables and finally flips protections to remount root RW.
AI-written summary · about
chapters (16)
- 0:00Introduction
- 1:19iOS jailbreak overview
- 2:11CVE-2016-7637 explained
- 8:37Generation number manipulation
- 14:36Kernel privilege escalation via CVE-2016-7644
- 21:41Task port explanation
- 27:36Process privilege manipulation
- 31:10AMCC and kernel patch protection
- 34:40Bypassing AMCC
- 41:09Page table manipulation
- 42:15Virtual address mapping tampering
- 44:05Disabling code signature checks
- 45:55Sandbox disabling
- 47:00Bypassing LwVM
- 48:27Remounting root partition
- 49:39Summary and demo
related talks
 44mExploiting Unpatched iOS Vulnerabilities for Fun and Profit
 50mRo(o)tten Apples: Vulnerability Heaven in the iOS Sandbox
 36mState Of IOS Jailbreaking In 2025
 43mDebug for Bug: Crack and Hack Apple Core by Itself
 29miOS Runtime Manipulation (PWND)
 54mSubverting Apple Graphics: Practical Approaches to Remotely Gaining Root
 01h 01mHow to Break AI Systems (Before Someone Else Does)
 35mAttacking iPhone XS Max