Attacking iPhone XS Max

summary
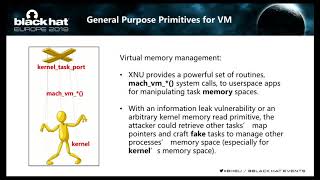
Identifies an XNU Unix domain socket race that creates a use‑after‑free via UNP bind temporary unlock and shows a concrete exploit chain: close sockets, trigger zone GC, spray controllable OSData and pipe buffers, replace freed memory with OOL port descriptors to build a fake kernel task/TFP0, then achieve arbitrary kernel read/write and KASLR leak. Shows PAC on A12 blocks direct ROP, and bypasses it by abusing saved thread context and invoking a PPL entry to load a trust cache, yielding a working iPhone XS Max jailbreak and SSH.
AI-written summary · about
chapters (16)
- 0:00Intro
- 1:10Outline
- 2:03Unix Domain Socket
- 5:41Race Condition
- 9:56The fix
- 10:39The pattern
- 11:45UAF, let's look at the USE
- 12:32Binary version may be better
- 17:40PAC (Pointer Authentication Code)
- 21:51UAF, let's look at the second USE
- 25:49Got troubles while adding trust caches
- 27:42tfpo's write capability for kernel image
- 29:04Look for unprotected control flow transfer points
- 32:07What can we do
- 33:18Got ssh on iPhone XS Max
- 33:40Black Hat Sound Bytes
related talks
 37mAttacking The XNU Kernel In El Capitain
 50mRo(o)tten Apples: Vulnerability Heaven in the iOS Sandbox
 37mEternal War in XNU Kernel Objects
 40mIntroduction into Reverse Engineering and iOS Security
 50mFinding Vulnerabilities In iOS/MacOS Networking Code
 54mSubverting Apple Graphics: Practical Approaches to Remotely Gaining Root
 44mExploiting Unpatched iOS Vulnerabilities for Fun and Profit
 29miOS Runtime Manipulation (PWND)