Reverse Engineering WhatsApp Encryption for Chat Manipulation and More
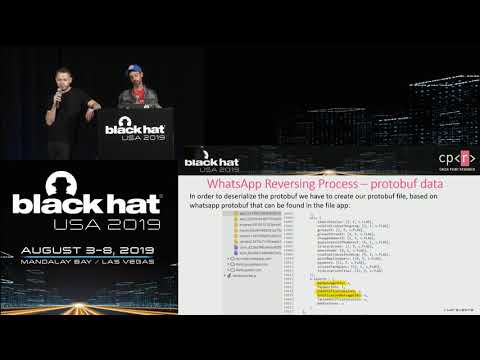
summary
Reverse engineers recover WhatsApp Web keys, translate its JS crypto into Python and build a BurpSuite extension that parses the 144-byte secret, performs ECDH + HKDF, verifies HMACs, and uses the extracted AES key to decode protobuf + AES-CBC payloads. They demonstrate live manipulation: change message content, spoof the sender/fromMe flag, inject users into groups and quote-reply as others; one group-targeting bug gets patched. Claims: full local decryption and on‑the‑fly outbound protobuf tampering works with captured web keys.
AI-written summary · about
chapters (8)
- 0:00Introduction
- 1:22Infrastructure and risks
- 3:36Encryption architecture
- 7:00Cryptographic breakdown
- 10:56Message manipulation logic
- 13:31Tooling and implementation
- 16:51Live demonstration
- 21:21Conclusion
related talks
 29mPwning WhatsApp The Dark Side Of Web based Messaging Apps
 32m(In)Secure Messaging Apps: A Lateral Movement Into Your Privacy
 39mUsing WhatsApp as a Command Line ( Breaking out of the walled Garden)
 40mEnd-to-end encryption: Behind the scenes
 19mBuilding private products
 01h 07mBuilding Rock-Solid Encrypted Applications
 19mPrekey Pogo: Investigating Security and Privacy Issues in WhatsApp's Handshake Mechanism
 31mAnti-Forensics: Reverse Engineering a Leading Phone Forensic Tool