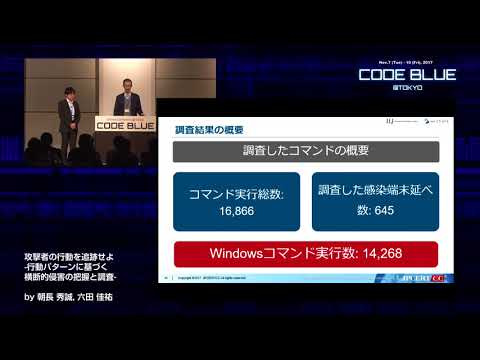
Track the Attacker’s Actions — Understanding and Investigating Cross‑Cutting Intrusions Based on Behavior Patterns
summary
The talk analyzes lateral-movement behaviors used in targeted intrusions by examining attackers’ C2 servers and malware communications to reconstruct post-compromise actions. It identifies common attack patterns and a small set of tools reused across campaigns, shows that Windows default auditing typically misses useful execution traces, and describes how to detect or investigate incidents by tracking use of those tools and adjusting logging/audit settings.
AI-written summary · about
chapters (11)
- 0:00Introduction
- 4:09Attacker behavior patterns
- 6:20Analyzing attack tools and commands
- 11:54Windows command usage
- 18:10Lateral movement and log wiping
- 25:29Logs and evidence collection
- 31:03PowerShell logging setup
- 36:11Audit policies and Process Monitor
- 41:31Log usefulness and recording
- 47:46Log tampering prevention and forwarding
- 50:19Summary
related talks
 35mEnhancing Operations Through the Tracking of Interactive Linux-based Intrusion Campaigns
 40mFighting Where They Aren't: How Attackers Avoid Endpoints in Modern Attacks
 26mTechnical Tracks
 27mBreach - ATT&CK - Osquery
 34mKeynote: Multiplying Threat Intelligence
 21mThe New Ground Truth for Security
 48mLateral Movement in the Age of Hybrid Cloud
 48mHacking Exposed: Next-Generation Tactics, Techniques, and Procedures