A New Era of SSRF - Exploiting URL Parser in Trending Programming Languages!
summary
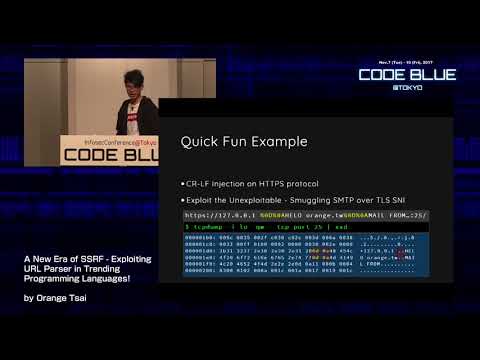
Demonstrates a practical exploit chain that turns URL parser inconsistencies into SSRF bypasses and real RCE: a custom fuzzing tool finds parsing mismatches across Python, PHP, Perl, Ruby, Java, JavaScript, Wget and cURL, yielding 20+ zero days in libraries and apps (WordPress, vBulletin, MyBB, GitHub). Shows concrete bugs — curl vs. PHP parsing, double URL decoding, Unicode and SNI hostname tricks, space/newline injections — and a working GitHub Enterprise demo that uses protocol smuggling + memcached object injection to achieve remote code execution.
AI-written summary · about
chapters (13)
- 0:00Intro
- 1:30About Orange Tsai
- 5:15Protocol Smuggling in SSRF
- 6:26Quick Fun Example
- 12:05URL Parsing Issues
- 19:21NodeJS Unicode Failure
- 22:31GLibc NSS Features
- 29:34Abusing IDNA Standard
- 31:21Abusing URL Parsers - Case Study
- 36:28Protocol Smuggling - Case Study
- 46:07Bug Bounty - Case Study
- 47:19Mitigations
- 48:05Summary
related talks
 47mA New Era of SSRF - Exploiting URL Parser in Trending Programming Languages!
 42mModern web application bugs
 58mModern web application bugs
 50mModern WebApp Vulnerabilities
 47mLive Hacking: Breaking into Your Web App
 56mModern Web Vulnerabilities 2020
 41mLive Hacking: Breaking into Your Web App
 45mKnow Your Enemies: Live Exploit of a PHP Engine Security Breach