Modern Web Vulnerabilities 2020
summary
Demos show an ESI injection where SVG uploads force the reverse proxy to fetch internal pages (PNG is blocked, SVG succeeds), enabling content theft, XSS or cookie leakage; a prototype pollution exploit corrupts server-side objects, escalates to admin session values and achieves RCE by poisoning NODE_OPTIONS to require /proc/self/environ and spawn a reverse shell; GraphQL traversal exposes unauthorized records (one bounty reported at $20,000); an HTTP desync/request-smuggling chain mixes chunked and content-length headers to make a backend accept attacker-supplied requests (Burp and James Kettle tooling helped; one bug earned $500).
AI-written summary · about
chapters (18)
- 0:00Intro
- 0:34NDC Security 2018
- 1:49Insecure Deserialization
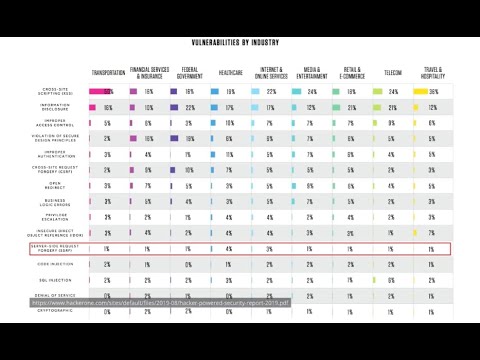
- 2:19SSRF - Server Side Request Forgery
- 5:33Edge Side Includes
- 6:14Reverse proxy with caching
- 11:17Dangers of ESI Injection
- 12:08Finding and stopping ESI injection
- 13:11JavaScript prototypes
- 13:55Example: Logger definition
- 14:44Exploring prototypes
- 16:02Prototypes are mutable!
- 17:41Common JavaScript patterns
- 22:40Attack vectors
- 28:02Avoiding prototype pollution attacks
- 30:16Common API Problems
- 41:43Classic HTTP Request smuggling
- 49:35Detection and protection


