Avoiding cloud security anti-patterns the right way

summary
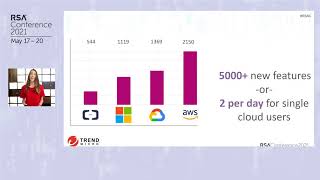
Research finds 65% of cloud incidents from misconfiguration and reports concrete exposures: 56% of organizations have SSH open, 39% expose RDP, and 61% still offer TLS 1.1. Scanning across providers finds ~34 million vulnerabilities, about 3.2M exposed hosts with ≥1 vuln and 1M hosts with ≥10; half of vulns are older than two years. Exploits compress to a median ~6 days from disclosure and 35% appear within a week. Demonstrations use Prisma Cloud resource query language, STIX/TAXII threat feeds and PAN‑OS integration to detect, alert and automatically block malicious infrastructure (tests show IOC ingestion and firewall rules enforcing successful containment).
AI-written summary · about
chapters (20)
- 0:00Intro
- 0:32Agenda
- 1:26Antipatterns
- 2:32Misconfigurations
- 3:20AWS Shared Responsibility Metrics
- 5:42Entropy of Cloud
- 9:58Traditional Application Service
- 14:13Vulnerabilities
- 16:32Vulnerability age
- 17:49Number of vulnerable
- 21:03Historical trend of exploit development
- 22:49AWS lagging behind
- 24:02Rock history
- 27:32Rock statistics
- 29:35Palo Alto Threat Group
- 30:56Bad Network Connection
- 32:35Prisma Cloud Demo
- 39:42Prisma Query Language
- 41:12Prisma Resource Query Language
- 47:46VM Series
related talks
 18mSecuring cloud innovation: Lessons learned
 46mStories from the cutting edge: Cloud security in 2023
 40mWork Smarter Not Harder: Tips to Approach Cloud Security the Easier Way
 43mClouds in the forecast: CrowdStrike cloud risk report
 41mIdentifying and Mitigating Cloud and Container Threats
 25mTrust in the edge, trouble in the cloud
 37mShift left, shield right: Code-to-cloud strategy for securing apps
 31mCloud Threat Landscape - 2021