Securing Your Java Containers by Breaking In
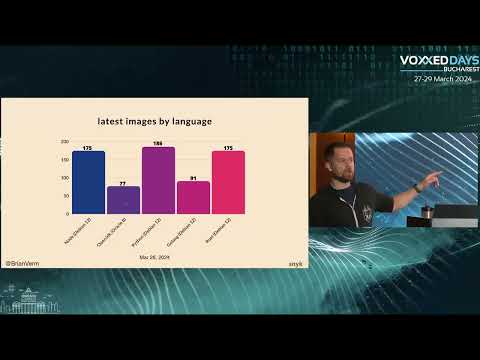
summary
Shows live breakins: ImageMagick in a base image allows RCE via crafted images, Apache Struts + Tomcat 8.5.2 yields an uploaded JSP webshell, Spring Data REST versions allow expression-language RCE. Demonstrates shrinking a 1.03 GB JDK+Maven image to 270 MB with multi-stage builds and creating a minimal runtime with jlink + jdeps. Warns that a pulled Tomcat image has ~735 vulnerabilities (70 critical) and updating it drops that to 28 with no critical/high. Advises scanning and continuous rebuilds with sneak container test and never running containers as root.
AI-written summary · about
chapters (7)
- 0:00Introduction to containers
- 4:37Choosing the right base image
- 14:37Optimizing image size
- 23:14Applying least privilege
- 27:02Continuous security scanning
- 30:29Handling framework vulnerabilities
- 43:40Architectural best practices
related talks
 46mStranger Danger: Securing Your Java Containers by Breaking In
 40mSecuring Containers by Breaking in
 47mMission Possible: The 45-Minute Path to Bullet-Proof Java Container Images
 47mSecuring Containers By Breaking In
 37mSecuring Containers by Breaking In
 35mSecuring Containers by Breaking In
 50mStranger Danger: Your Java Attack Surface Just Got Bigger
 02h 38mJava application security the hard way - a workshop for the serious developer