Securing Containers by Breaking in

summary
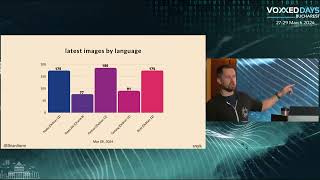
Live demo exploits an ImageMagick RCE to escalate from an uploaded JPEG to a shell, proving containerized apps inherit OS flaws. Research shows Node images >500 vulns and plain Ubuntu ~30; OpenJDK variants: Ubuntu 22, Debian 73, Alpine 0 in the demo. Scanning with Snyk container test and continuous monitoring finds issues; switching base images fixes ~40% of vulns and rebuilding fixes ~20%. Recommendations: run as non‑root, use hadolint, and prefer multi-stage build shrinks 631MB → 132MB.
AI-written summary · about
chapters (5)
- 0:00Start
- 2:22Best Practices for Docker Image Security
- 7:59# Find, Fix and Monitor Open Source Vulnerabilities in the OS
- 12:0444% of docker image vulnerabilities can be fixed with newer base images
- 24:14# application dependencies impact container security too
related talks
 47mSecuring Containers By Breaking In
 35mSecuring Containers by Breaking In
 52mSecuring Your Java Containers by Breaking In
 37mSecuring Containers by Breaking In
 46mStranger Danger: Securing Your Java Containers by Breaking In
 49mVulnerability Exploitation In Docker Container Environments
 32mSecure containers - Michael Wager and Michael Helwig
 41mLive Hacking: Breaking into Your Web App