Two Round MPC via Multi-Key FHE
summary
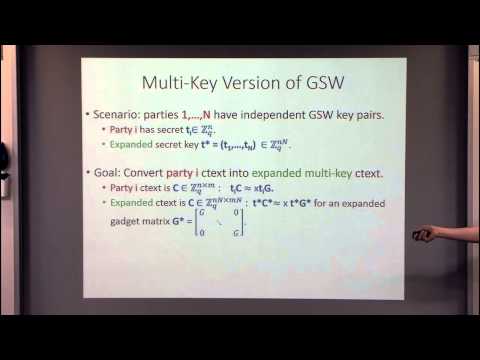
Constructs two-round MPC from LWE by simplifying a GSW-style multi-key FHE so independent public keys encrypt into an expanded ciphertext space, then homomorphically combines them and runs a one-round distributed decryption that sanitizes with a gadget inverse and sums partial decryptions with added noise. The protocol targets semi-honest security (adds NSX for malicious), requires a common random string for key-pattern alignment, tolerates up to all-but-one corrupted parties as presented, and is concrete and implementable.
AI-written summary · about
chapters (14)
- 0:00Intro
- 0:19Multi-Party Computation
- 0:47Motivating Questions
- 1:32Round Complexity
- 2:46MPC from FHE
- 4:38MPC from Multi-Key FHE
- 8:20Gentry-Sahai-Waters FHE
- 8:46The GSW FHE: Key Generation
- 9:41The GSW FHE: Encryption
- 11:37The GSW FHE: Evaluation
- 12:51Multi-Key Version of GSW
- 14:49Ciphertext Expansion
- 21:12One-Round Distributed Decryption
- 24:25Putting it all together
related talks
 01h 01mMulti-key FHE and Spooky Encryption
 29mTowards Scalable Constant-Round MPC from Minimal Assumptions via Round Collapsing
 01h 01mCircularity Based IO, Part 1
 01h 04mFully Homomorphic Encryption II
 45mFully Homomorphic Encryption I
 58mSecure Multiparty Computation I
 30mOn the Optimal Round Complexity of Multi-Party Computation in the Plain Model
 01h 07mLattices and Encrypted Computation