Ransomware in ICS: Impacting Critical Infrastructure and Operations
summary
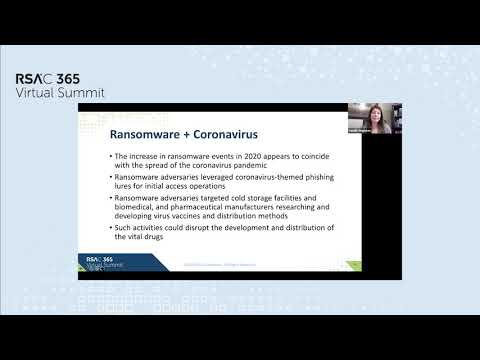
Ransomware attacks against ICS-connected organizations increase 500% from 2018–2020 across 220 incidents, with 56% causing operational impacts like plant shutdowns, shipping delays and layoffs; manufacturing receives over one third of hits and North America 45%. Operators shift to human-operated campaigns (phishing, exposed RDP, VPN/exploit chains) and double extortion—steal data then ransom—seen in strains such as EKANS and groups using Ryuk at Evraz case tactics. Defenses: architecture reviews, strict IT/OT segmentation, MFA, daily tested backups and alternate recovery sites.
AI-written summary · about
chapters (15)
- 0:00Intro
- 0:35Presentation Outline
- 1:22Ransomware Overview
- 2:23Ransomware Research Data
- 3:09Ransomware History
- 5:12Ransomware + Coronavirus
- 9:26Impacts to Operations
- 11:10ICS Specific Ransomware
- 12:13Ransomware OT
- 13:28Human-Operated Ransomware
- 17:29New Trend: Extortion
- 18:24Extortion Risks and Consequences
- 20:49ICS Impact of Extortion
- 22:00Future Predictions
- 23:34Defensive Recommendations
related talks
 26mFrom Existential to Reality: 3 Experts on the Evolution of ICS Threats
 48mRansomware: From the Boardroom to the Situation Room
 29mNo More Ransomware in Critical Infrastructure!
 40mRansomware Threat Landscape
 52mRansomware; The Real Pandemic
 37mRansomware Resilience: Holistic Defense for SOC Leaders
 51mPreparing for and Defending OT Systems from Ransomware
 37mThe 2024 Ransomware Threat Landscape: What's Fueling the Epidemic?