Make your Angular app a max security prison
summary
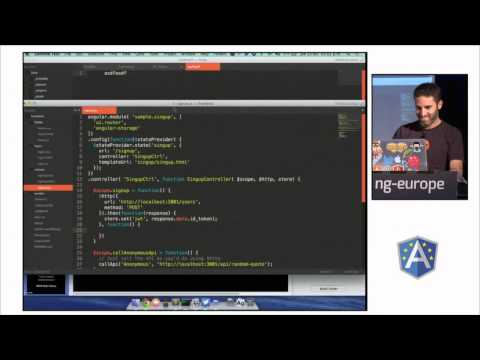
Demo builds a tiny Angular SPA plus a Node backend that issues JSON Web Tokens and it actually works after some typos; implementation shows signup/login endpoints that return an ID token, storing it in localStorage via Angular storage, attaching it to every request with an JWT interceptor, and protecting routes by checking token presence and expiry with Angular-JWT. Live coding includes the exact curl/data flow: header = Authorization: Bearer <token>, token signature validation on the server, and rejection when signatures or secrets mismatch.
AI-written summary · about
chapters (9)
- 0:00Modern auth challenges
- 2:16Token-based auth needed
- 8:02How JSON Web Tokens work in practice
- 11:06Live coding setup
- 19:33Login and token storage
- 24:02Sending tokens with API
- 27:35Protecting routes in SPA
- 30:47Decoding token client-side
- 32:32Closing remarks
related talks
 39mLogin and Access Control in Angular
 19mAngular's User Authentication Tool Belt
 28mA Token Walks Into a SPA...
 46mThe Amazing Angular 2
 26mAngular Router Authentication and Authorization Real LIVE LIVE LIVE LIVE LIVE Demo
 25mAuthstronomy: The Science of Authenticating Angular Apps
 26mThe Science of Authenticating Angular Apps
 30mThe science of authenticating Angular apps