Edge Security in Untrusted IoT Environments
summary
Demonstrates a concrete edge security design that uses HashiCorp Vault as a PKI and secrets broker to issue short‑lived X.509 certs (mTLS) for OpenVPN endpoints and to mint scoped AWS credentials for per‑user S3 backups. Architecture uses Kubernetes + Vault Agent Injector for server certs, a Vault agent + consul-template on Home Assistant clients to render ca/crt/key, 90‑day cert TTL with earlier aggressive 6‑hour rotation changed due to flaky networks, and per‑user AWS STS policies — solution works with operational tweaks.
AI-written summary · about
chapters (13)
- 0:00Intro
- 1:01About me... Smart Homes
- 2:32THE CORONAVIRUS GET HERE QUICKER
- 3:08Powered by awesome!
- 3:39Proudly Powered by Home Assistant
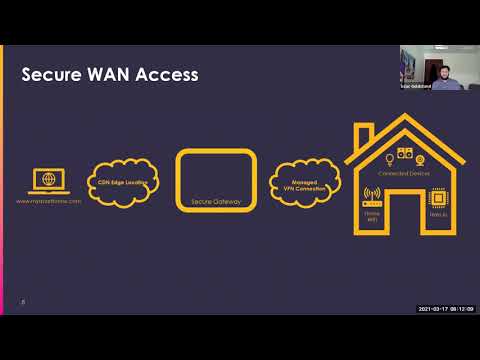
- 5:51Secure WAN Access
- 7:59HashiCorp Vault Dynamic secret management
- 9:20Home Assistant Add-On Model
- 11:50Session Authentication - Foundation
- 19:25VPN Client
- 28:14Secured centralized backups
- 34:34Untrusted Edge... Doesn't matter
- 35:35For more information...
related talks
 42mZero Trust security with HashiCorp Vault and AWS (PRT239)
 28mSecret Management with Hashicorp´s Vault
 38mKeeping Secrets - A Practical Approach to Managing Credentials
 29mKeys, Certs and Vault: From DevSecOps to Post-Quantum
 43mSecret Management with Hashicorp's Vault
 45mSecure Together: Consul + Vault
 01h 03mSecuring Legacy Applications and Container Microservices in Kubernetes
 42mZero-Knowledge Architecture, or Leak-Free Secrets, with HC Vault