Sandboxes all the way down - A hitchhiker's guide to platform...
summary
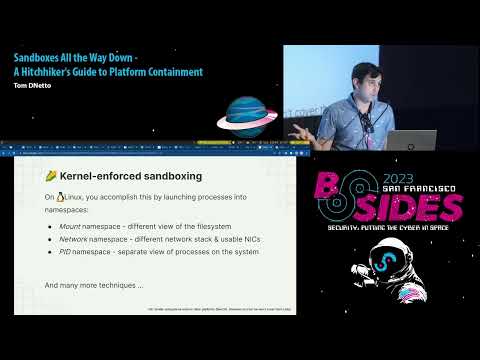
Survey of containment techniques claims kernel isolation is easy to deploy but routinely leaks via kernel bugs, so combine it with purpose-built mediators like gVisor which emulate syscalls but miss some calls and slow IO. The strongest boundary is a VM: firecracker (used by AWS Lambda) plus an Alpine image, a virtio socket for host shell access, and a network namespace on the host to enforce egress rules. Demo notes: firejail example maps root to UID 1000 and VMs need careful image and network integration.
AI-written summary · about
chapters (8)
- 0:00Start
- 0:36The need for platform containment
- 2:28Main sandboxing techniques
- 3:52Kernel-enforced sandboxing
- 10:38Syscall emulation
- 13:56Virtualization: Getting started
- 14:33Virtualization: Integration is challenging
- 16:09Virtualization: Worked example
related talks
 43mSandboxes, Seccomp, and Syscalls: Chasing Isolation in Kubernetes (Mark Manning)
 14mYour Containers Aren’t Alone: Demystifying Container Isolation
 01h 25mSandboxing a Linux Application
 31mYour Containers Aren’t Alone: Demystifying Container Isolation
 47mContainer Security
 19mSandbox to confidential containers: A brief on the evolution of container isolation
 42mSandboxing a Linux application
 45mMaking Containers Safer