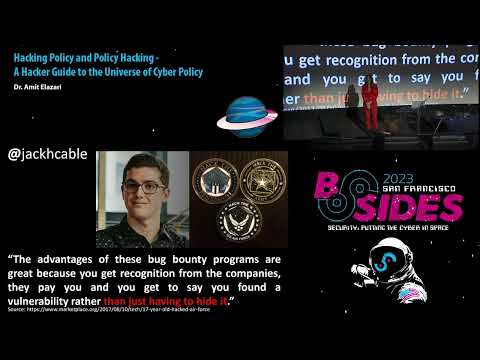
Keynote: Hacking Policy and Policy Hacking - A Hacker Guide to...
summary
Describes how targeted actions — a GitHub repo of bug‑bounty contracts, a public “hall of fame” for safer terms and the disclose.io playbook — move companies from 17 → thousands adopting researcher-friendly language, trigger a DHS binding directive in 2020, and get academic work cited by the Supreme Court in 2021. Shows concrete tools (contract templates, vulnerability disclosure programs, a Security Research Legal Defense Fund, Hacking Policy Council) and outcomes (platform safe‑harbors, a $120M Google settlement cited) and launches an Open Policy platform.
AI-written summary · about
chapters (6)
- 0:00Introduction and background
- 2:40Hacking and enforcement
- 8:21Legal safe harbors
- 20:59Evolving regulatory landscape
- 27:09Hacking law and advocacy
- 38:57The future of policy
related talks
 33mHacking the Law: Are Bug Bounties a True Safe Harbor?
 36mKeynote: We Deserve Rights
 25mEverything Old Is New Again: Legal Restrictions on...
 51mBug Bounty: Keeping Hacks Ethical in 2022
 56mKeynote: AppSec: From Outsiders to Allies
 16mKeynote: There Is Just One Way to Do Open Source Security: Together
 23mIntroduction to security research and bounty hunting on Apple's platforms
 37mSecurity Culture Hacking: Disrupting the Security Status Quo