Sharks in the Water: Open Source Component Risk and Mitigation

summary
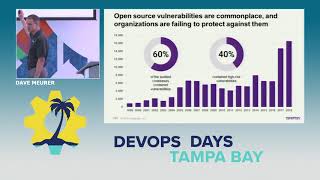
Open source components explode in volume — roughly 22,000 new releases per day since 2018 and NPM alone supplies most app code — and risk follows: enterprises pull ~313,000 OSC releases per year, 28,000 have vulnerabilities, 18,500 score CVE ≥7 and 8,000 score ≥9, and OSS factors in about 31% of breaches. Practical mitigations shown are scanner selection (don’t build your own), ingestion APIs, dashboards, GitHub security alerts, bots to auto-update direct deps, lockfiles to tame transitive chains, and monthly cross‑team reviews to act on prioritized findings.
AI-written summary · about
chapters (6)
- 0:00Introduction and speaker background
- 1:08Component risk landscape overview
- 6:54Trusting teams and shared responsibility
- 12:11Automation and scanning strategies
- 21:59Vulnerability remediation process
- 23:42Q&A and closing remarks
related talks
 41mManaging the risk and growth of using Open Source Software
 30mDevSecOps: Understanding Open Source Software risk in your applications
 38mApplication Security in the age of Open Source
 31mThe Value of OSS Management for Risk Mitigation
 45mPanel Discussion: Managing Open Source...
 30mOpen Source Malware or a Vulnerability? The Philosophical Debate and How To Mitigate
 38mBetter, Faster, Stronger: How the Global Acceleration of OS Development Is Changing
 41mManaging the Risk of Software Supply Chain Attacks