Profiling "VIP Accounts" Access Patterns in User-Centric Data Streams
summary
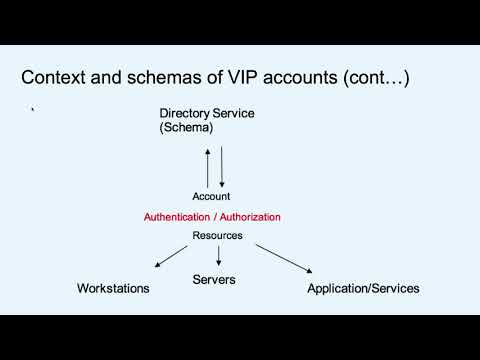
Real-time pipeline ingests Active Directory and Kerberos events via Kafka Streams and builds per-account graphs scored with PageRank + SVD; anomaly detection compares the top eigenvalue of a user's time-bucket matrix day-to-day and flags deviations above a tuned threshold. Prototype fingerprints VIP behavior (backups, password resets, account creation, installs), scales per account, surfaces a small set of high-risk accounts, and leads to actionable alerts that previously required ~20 hours to validate and produced two prosecutable insider cases.
AI-written summary · about
chapters (8)
- 0:00Introduction to VIP profiling
- 1:52Defining VIP accounts and risks
- 7:12RBAC and Active Directory basics
- 11:53Targeting VIP account behaviors
- 14:01Technical implementation with Kafka
- 21:37Modeling VIPs and anomaly detection
- 25:35Algorithm prototype and limitations
- 27:25Q&A and conclusion
related talks
 52mDevil in the Haystack
 49mA Real-World Example of Using Network Behaviour to Detect Cyber-Compromise
 31mLog In Through the Front Door: Automating Defense Against...
 16mMost Effective Tactics to Combat Account and Platform Fraud
 16mAnalysing Real time Activity Streams for Security
 48mHunting Stealth Adversaries with Graphs & AI
 56mRecreating the State of the Player
 40mBridging voter data and social data using Apache Streams