Containers, Kubernetes and Practical DevSecOps
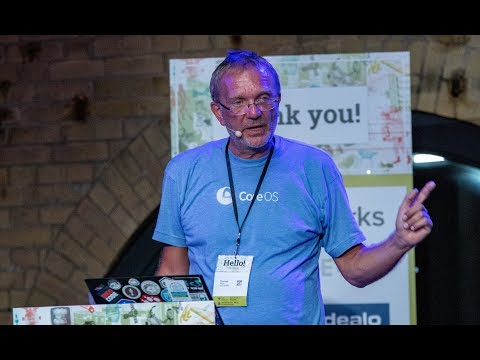
summary
Kubernetes contains the primitives to secure microservices but default deployments leave gaps: audits find misconfigured RBAC, exposed sockets, and databases running in containers that break backups and restores. Practical fixes shown include network policies to limit lateral movement, TLS sidecar proxies and Istio for transport-level zero trust, using runtimeClass and SELinux to reduce privileges, and opting for multi-cluster or OpenShift tenancy rather than ad hoc single clusters. Examples come from medical, energy, traffic and telephony environments and report whether each change prevented the noted failures.
AI-written summary · about
chapters (7)
- 0:00Introduction
- 10:02Containers vs virtual machines
- 17:21Security in container environments
- 26:18Common container mistakes
- 33:05Securing databases in containers
- 38:19Network security for containers
- 40:19Q&A session
related talks
 46mContinuous Kubernetes Security
 28mContainer Security: A Horror Story
 43mKubernetes Security: Attacking and Defending Modern Infrastructure
 35mKubernetes Security - Challenge and Opportunity?
 33mKubernetes Security Jumpstart
 22mSecuring Kubernetes: Best Practices for DevSecOps in the Cloud-Native Era
 25mSecuring Kubernetes Multi-Tenancy: Navigating Challenges Through DevSecOps Control and Visibility
 43m6 Strategies to Bring Order to Kubernetes Security Disruptions