Attack API Architecture
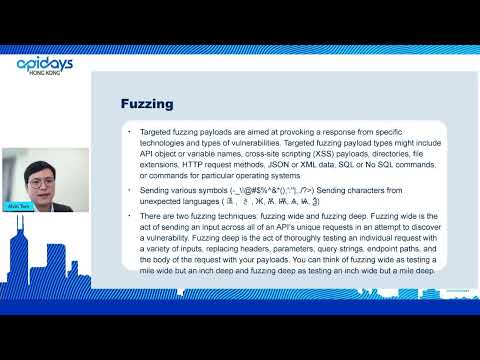
summary
APIs that favor developer convenience become attack surfaces because hackers exploit hardcoded mobile creds, outdated packages and predictable tokens to pivot from one component to the rest. Examples include OTP brute‑force via the password reset API, token guessing when IDs are sequential, and mass assignment that promotes low‑privilege accounts to admin. Defenses shown are API gateways, WAF/ingress controls, AI/ML anomaly detection, strict authz, response masking and long audit logs to spot slow distributed botnets probing thousands of endpoints.
AI-written summary · about
chapters (13)
- 0:00Introduction
- 1:33API security importance
- 3:21Common API vulnerabilities
- 6:53Authentication attacks
- 10:05Exploiting API errors
- 13:17Authorization flaws
- 15:06Mass assignment issues
- 16:11Insecure object references
- 18:15Cross-site scripting in APIs
- 19:37API security responsibility
- 22:05Robust API security architecture
- 26:01Steps to secure APIs
- 29:11Summary
related talks
 25mHow Do They Get In?! Understanding the API Attack Vector
 51mThe Next Application Security Frontier: AI-Ready API Defense
 50mAPI Abuse through Mobile Apps: New Attacks, New Defenses
 31mAPI security
 35mClosing Keynote Day 1 API First Hacking
- 50mAPI Abuse through Mobile Apps: New Attacks, New Defenses
 25mThe New API Vulnerability Frontier
 39mThe API Assessment Primer