Practical security for Android apps
summary
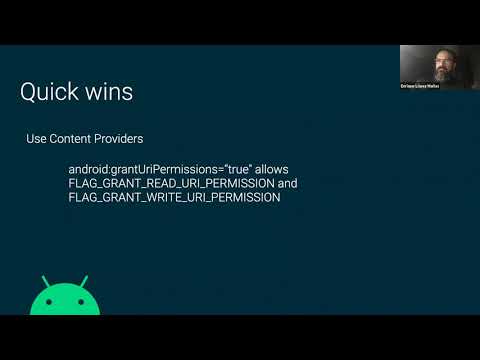
Covers concrete fixes and failures: enforce TLS (demonstrates Charles revealing plaintext), use AndroidX EncryptedFile with MasterKey for local data, set contentProviders exported=false and validate external files, prefer parameterized SQL and short‑lived tokens over stored credentials, and enable certificate pinning (but notes Frida and Objection can bypass naive pins). Shows hands‑on reverse engineering—decompile‑recompile demo that edits an APK and reinstalls—proves practical attacks and which mitigations actually work.
AI-written summary · about
chapters (10)
- 0:00Introduction
- 1:38What is security
- 3:38WhatsApp
- 6:31Swiftkey
- 7:33Facebook
- 13:41Google Play
- 15:20Cryptography
- 19:12Reverse Engineering
- 22:29Demo
- 32:47Questions
related talks
 29mSecuring Android: Tackling Advanced Threats and Enhancing App Security
 34mSecuring Android: Tackling Advanced Threats and Enhancing App Security
 34mDemystifying Android Security
 28mSecure Development whit Android
 29mSecuring Android Applications - The not so se…
 01h 02mDon’t get stung by OWASP: An intro into writing code for greater Android Security
 47mSecuring Android Applications, The Right Way
 43mAttacking Android Applications