Open Source Compliance

summary
Covers open-source compliance fundamentals: why copyright and license texts matter and specific technical controls such as generating an SBOM/SPDX for every product, running automated license scanning in CI, preserving copyright notices and disclaimers, and recording provenance for each dependency. Recommends an operational compliance management system with defined roles and board-level responsibility, plus periodic audits and triage procedures so teams can identify, fix, or replace components with risky or noncompliant licenses.
AI-written summary · about
chapters (13)
- 0:00Intro
- 0:12Agenda
- 1:23Background: Copyright
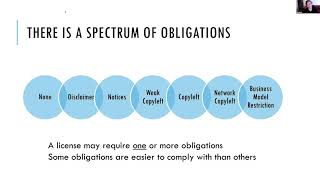
- 4:01Open Source licenses
- 4:47Example: Notices
- 5:53Example: Copyleft
- 6:21Software Compliance
- 7:38License violation
- 9:03Legal Consequences
- 9:45Responsibility
- 14:21Reality
- 15:45OpenChain
- 20:12Questions?
related talks
 01h 38mOpen Source Licensing: Types, Strategies and Compliance
 15mShifting Open Source Compliance Activities Left
 29mOpen Source and IP Departments: Risk Containment and Portfolio Management
 32mOpen Source Contributions in Today’s World
 51mOpen Source License Compliance
 31mOperationalizing Open Source Projects: When the Rubber Meets the Road
 25mEnsuring OSS License Compliance the Easy Way
 43mSoftware Licensing and Compliance: It's All About Community