Beyond Rate Limiting Adaptive Security for Python Web Applications

summary
Behavioral middleware claims to detect scraping and probing using concrete signals: header scoring, keyword/path probes, honeypot timing and UUID tamper checks, plus an isolation forest model that retrains roughly 100k requests per day → weekly, 1M → daily. The project ships as pip install AI WAF with an optional Rust accelerator, reports no noticeable slowdown in practice, and uses score thresholds and post‑request heuristics to decide blocking rather than opaque LLMs.
AI-written summary · about
chapters (7)
- 0:00Adaptive security for Python apps
- 1:35Validating HTTP headers
- 4:26Keyword validation vs probes
- 6:13AI anomaly detection
- 9:06Honeypot timing for bots
- 11:14UUID tamper analysis
- 12:59Q&A
related talks
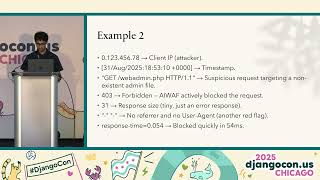 32mBeyond Rate Limiting: Building an Active Learning Defense... with Aayush Gauba
 27mSecuring Applications and Managing WAFs at a large scale
 37mWeb Application Firewall Bypassing
 47mReversing Engineering a Web Application - For Fun, Behavior & WAF Detection
 34mArchitecture of an Anti-Bot Protection
 52mKnock Knock: Understanding Who is Using Your Web Applications
 50mArchitecture of an Anti-Bot Protection
 15mLevel up security: Advanced AWS WAF rules & bot detection techniques