Software Security Metrics
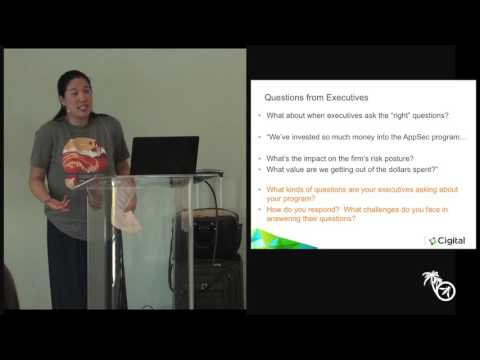
summary
Claims a practical method: start from 20 risk management objectives, pick relevant objectives, turn each into specific questions, and collect the data that answers them. Gives concrete metrics such as percentage of applications reviewed and signed off, pass rates for permit-to-build/permit-to-deploy gates, remediation timelines and defect counts by severity. Describes a tool under development that maps objectives → questions → required data and shows when new defect discovery raises expected bug counts and how fixes track to closure.
AI-written summary · about
chapters (18)
- 0:00Intro
- 4:40Agenda
- 5:10Questions from executives
- 10:27Why Metrics
- 11:07Risk Management Objectives
- 12:34Measurement vs Metric
- 14:48Phases of Metrics
- 16:51Defects
- 18:13Bad Scenarios
- 19:55Vanity Metrics
- 20:50Metrics Without Context
- 23:03Metrics With Executives
- 23:55Risk Management
- 29:03Policy Standards Outreach
- 30:39Software Environment
- 30:53Software Security Capabilities
- 40:23Risk Tolerance
- 43:14Coverage
related talks
 40mCybersecurity Metrics Development for Board and Risk Committee Reporting
 25mSecurity Metrics: Protecting Our Digital Assets of the Future
 27mProduct Security Vulnerability Management Metrics are Hard
 59mKeynote: Measure Security Effectively
 53mOver a Decade of Software Security: What Have We Learned
 01h 00mTop 10 Metrics for Successful DevSecOps Projects
 35mMetrics That Matter: How to Choose Cloud Security KPIs for Your Business
 53mMetrics that Matter.Confidence & Resilience in Your Security Program