Dependency Check Project

summary
Open-source SCA that started in 2011 and currently uses the NVD plus Sonatype’s OSS Index to find CVEs, with a Docker image at about 3.5M pulls and Maven/Gradle plugins and a GitHub Action that ships nightly-updated data. It actually wraps NPM audit, Retire.js and Bundler Audit, does evidence-based identification via Lucene matching, produces HTML reports with suppression rules, finds transitive deps when run as a build plugin, and still has ~350 open issues and some false positives/negatives.
AI-written summary · about
chapters (16)
- 0:00OWASP Dependency Check intro
- 1:52SCA tools evolution
- 4:44Dependency Check origins
- 6:08Tool design and language support
- 9:38Integrations and ecosystem growth
- 12:26Usage and adoption trends
- 14:32How vulnerabilities are identified
- 18:24Library identification challenges
- 23:17False positives and false negatives
- 26:46Setting up and configuring the tool
- 28:09Live demo
- 32:50Reading reports and suppression rules
- 37:27Use cases and applications
- 41:17SCA in security posture
- 42:43How to contribute
- 44:28Q&A
related talks
 29mFlagship Projects: Dependency-Check
 20mDependency Analytics
 34mDependency Track
 42mAssessing the Risk of Open-source Components Using OpenSSF's Scorecard
 18mSecuring Open Source in Nomura’s Software Supply Chain
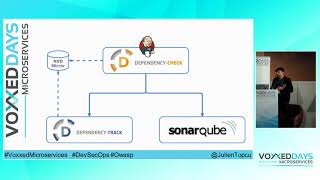 27mFind and Track the hidden vulnerabilities inside your dependencies
 41mManaging Audits for Critical Open Source Projects
 54mSupply Chain Sec /w Dependency Track