A Risk based Approach to API Security

summary
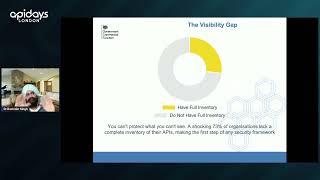
Claims concrete numbers: a cited survey shows 200% increase in APIs created and deployed and that one in four respondents suffers an API-driven data breach; 41% see incidents and 63% of those lead to data loss. Recommended controls are specific: automated API inventory, CI/CD security tests, NIST-style identify/protect/detect/respond/recover, runtime monitoring plus data-exfiltration detection because WAFs stop injection but not broken object level authorization or business‑logic abuse.
AI-written summary · about
chapters (7)
- 0:00Start
- 5:29Trends and figures
- 10:21Deconstructing Risk
- 16:01Risk Assessment: Determining Impact
- 18:40Risk Assessment: Determining Probability
- 32:32Threat Scenario
- 35:54Current API Security Challenges
related talks
 19mAvoid These API Security Pitfalls: Expert Insights
 22mLayered Approach of API Security Strategies and its Business Impact
 31mAPI security
 16mFuture-Proofing Your APIs: A Holistic Approach to Security, Privacy, and ROI.
 35mSecuring Your API: The OWASP Top 10
 26mAPI and Application Security - The Future
 31mStandard Classification: API Security Top 10 - A Beginner's Guide to Mitigation
 25mThe New API Vulnerability Frontier