Breaking the Next Factor - Evil will pwn you LIVE tonight

summary
Claims that there are more than a million MFA bypasses per month and that almost 70% of breaches involve a non‑malicious human hold up the argument, then live demos show full account takeovers via SIM swap, session hijacking and a reverse‑proxy man‑in‑the‑middle using services like evil proxy and tools such as EvilJinX. Concrete success rates and a step‑by‑step GitHub capture appear, plus practical mitigations: avoid SMS, add token binding, move MFA to sensitive operations, consider passkey adoption and detect MFA fatigue with short sessions and forced password resets.
AI-written summary · about
chapters (10)
- 0:00MFA vulnerabilities
- 6:29MFA bypass methods
- 8:17SMS OTP attacks
- 12:30MFA fatigue attacks
- 14:55MitM as a service
- 15:56Live GitHub hijack demo
- 28:06Reverse proxy deception
- 33:06Passkeys limitations
- 36:14Securing MFA systems
- 39:48Conclusion
related talks
 47mBreaking the Next Factor – Live Multi-Factor Authentication (MFA) Hacking
 40mPurple Team Auth: Hacking & Bypassing MFA Systems, and How to Armor Up
 26mMake MFA More Resilient
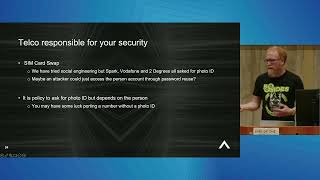 45mMFA: Stories that make you go 'Huh?'
 38mAnatomy of the Attack: The Rise and Fall of MFA
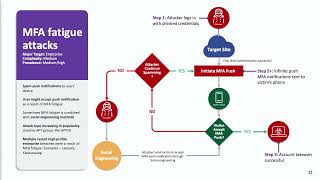 49mThe Death of Conventional MFA: How AiTM Attacks Are Changing the Game
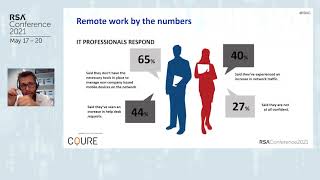 40mModern Identity Hacking: Have Hackers Really Adjusted to Constant Remote?
 48m2FA2Furious: New Threats to MFA