Breaking the Next Factor – Live Multi-Factor Authentication (MFA) Hacking

summary
Claims that MFA blocks most attacks sit beside a published figure of more than a million MFA bypass attacks monthly and Microsoft’s stopping-rate percentages. The demo uses man‑in‑the‑middle phishing proxies (examples named: Merina, Modishka, Evil Jinx), plus SIM‑swap, session‑stealer and MFA fatigue tactics, to harvest credentials, intercept authorization tokens and auto‑exfiltrate files. The live build intermittently lags but still captures passwords and session cookies enabling remote Outlook access and repository cloning when fully successful.
AI-written summary · about
chapters (20)
- 0:00Live MFA hacking intro
- 1:33Understanding MFA and its vulnerabilities
- 7:11Common MFA hacking methods
- 8:13SIM swapping demo
- 10:44Session hijacking explained
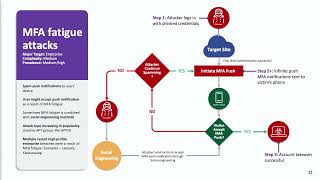
- 12:55MFA fatigue attacks
- 14:59MFA-as-a-service tools
- 16:26Target selection & intel
- 18:57Phishing lure crafting
- 20:00Live demo setup with Evil Jinx
- 23:22Phishing email sent
- 24:53Victim fake login interaction
- 26:21Credentials & tokens captured
- 32:16Session exploit on another machine
- 36:18Attack automation scripts
- 37:44Real-time MFA approval effects
- 38:28Fake login domain detection
- 39:09Defending against MFA hacks
- 41:19MFA best practices
- 42:03Q&A
related talks
 42mBreaking the Next Factor - Evil will pwn you LIVE tonight
 40mPurple Team Auth: Hacking & Bypassing MFA Systems, and How to Armor Up
 38mAnatomy of the Attack: The Rise and Fall of MFA
 26mMake MFA More Resilient
 45mMFA: Stories that make you go 'Huh?'
 49mThe Death of Conventional MFA: How AiTM Attacks Are Changing the Game
 40mModern Identity Hacking: Have Hackers Really Adjusted to Constant Remote?
 08mEnhancing Cybersecurity with Multi-Factor Authentication