SELinux: Myths and Realities

summary
Security-Enhanced Linux (SELinux) is presented as a practical, policy-based access-control module for Red Hat systems; the talk walks through simple examples to demonstrate SELinux features and how to use them to harden systems rather than disabling it. The presenter is a Red Hat content architect with extensive sysadmin and hardening experience who focuses on demonstrating SELinux’s usability and flexibility for system security.
AI-written summary · about
chapters (9)
- 0:00Welcome
- 1:45SELinux myths
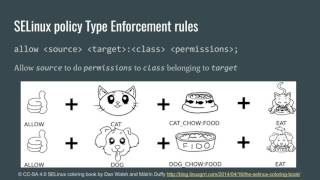
- 5:58Components and basics
- 9:05SELinux failure modes
- 14:03Modifying policies
- 18:19Demo: Fixing denied permissions
- 22:58Confined users
- 25:52Resources
- 26:35Q&A