Reverse-Engineering Driven Development

summary
Reverse engineering reveals concrete answers: disassemble macOS/iOS frameworks with Hopper disassembly + control-flow graph, attach with LLDB/Xcode debugging or extract caches with dsc extractor, and inspect registers and conventions. A real bug hinges on a 0.25 second event window (0.25 seconds event window) where a mouse-up within 250 ms routes to target/action instead of the framework popup; the implemented fix manually shows the popup and resolves the failure. Use a VM for unsafe work and consider debugserver on jailbroken devices.
AI-written summary · about
chapters (15)
- 0:00Intro
- 0:35Who am I
- 1:21Who is this talk for
- 2:06Why reverse engineering
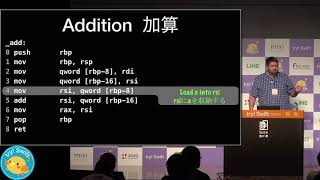
- 5:03Assembly language
- 6:45Assembly format
- 8:20Assembly code
- 9:52Registers
- 12:46Debugging
- 14:44iOS Debugging
- 17:36Disassembling
- 18:18Hopper
- 21:21Example
- 28:23Limitations
- 30:50Further Information
related talks
 20mAssembly. You can do it!
 27mHacking Marzipan
 19mJust Enough Objective-C
 05mMarzipan - UIKit on macOS
 05mMachObfuscator
 25mDriving View-State through Data for Fun and/or Debugging
 30mFrom Slow to Flow: Tips for Accelerating Your App Performance
 09mTracking user behaviour with ImpressionKit & SwiftHook for method swizzling ...