Explore invalid memory access
summary
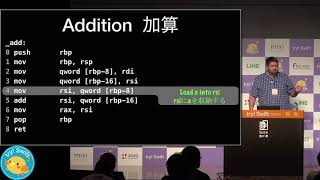
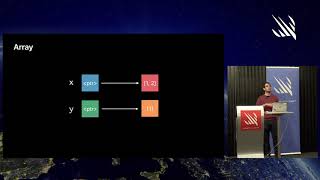
Shows how crashes are traced to concrete causes: use of the Hopper disassembler to map crash-report offsets to ARM64 instructions, reading register state (x0, x1, x16) and exception addresses, and finding a use-after-free in objc message send via selector/requestIdMap offsets. Demonstrates a Swift case where concurrent appends cause an invalid address (array append race), and proves fixes: serialize via a dedicated queue or add a lock to eliminate the swift array race.
AI-written summary · about
chapters (13)
- 0:00Intro
- 0:36Crashes by Invalid Memory Access
- 0:55IDENTIFY PATTERN
- 1:47HOW TO DEBUG?
- 3:13GET MORE FROM CRASH REPORT
- 5:26WHAT HAPPENED IN MESSAGE SEND FUNCTION
- 8:51CHECK REGISTER STATE
- 9:51ABOUT ISA
- 10:40WHO IS DEALLOCATED OBJECT?
- 11:48BASE ADDRESS + OFFSET
- 12:55TRACE ARGUMENTS
- 13:53TRACE THIS VARIABLE
- 19:59WRAP IT UP