D2T1 - Uncovering the Android Patch Gap
summary
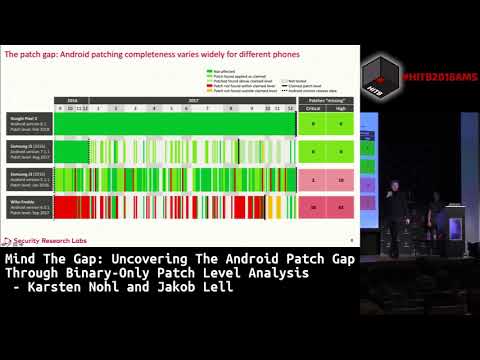
Research measures which Android security patches actually appear in firmware by comparing extracted function code to precompiled signatures built from patched and unpatched source trees, across about 1,100 source variants and 74 compiler configurations. Results cover 164 heuristic tests for userland fixes (from ~300 high/critical items), run against hundreds of firmware images and thousands of phones, and show many vendors omit patches (some devices miss a dozen+), with verification available via a sideloadable Android app that runs the checks locally.
AI-written summary · about
chapters (17)
- 0:00Introduction to Android
- 5:31Defining the research scope
- 9:00Patch analysis results
- 12:57Binary analysis method
- 16:56Engineering challenges
- 18:49Custom file system
- 20:21Candidate selection
- 21:06Signature generation
- 22:10Finding functions
- 23:37Rolling checksum algorithm
- 25:38Data processing flow
- 26:39Vendor patch quality
- 29:30Android security landscape
- 33:43Exploitation vs patch gaps
- 37:39Exploit chain complexity
- 39:37Conclusion and Q&A
- 45:12Future research and tools
related talks
 53mThe Art of Defense - How Vulnerabilities Help Shape Security Features and Mitigations in Android
 25mHarvesting Inconsistent Security Configurations in Custom Android ROMs...
 42mAndroid: Protecting the Kernel
 08mTechnical debt
 23mPrecise and Accurate Patch Presence Test for Binaries
 47mAdaptive Kernel Live Patching: An Open Collaborative Effort...
 47mSecuring Android Applications
 43mSecurity in Android Applications