How secure are Docker containers?

summary
Docker shows concrete protections: cgroup limits for CPU/memory/IO, no-new-privileges and seccomp profiles via a JSON syscall whitelist, AppArmor profiles and read-only containers to prevent filesystem tampering. Real incidents include an exposed Elasticsearch instance that generates ~568 Mbps outbound traffic by executing Java via the API, and a public Docker registry leak where downloaded images revealed source — reported and rewarded $10,000. Audit with Docker bench and compare container diffs to images to detect compromises.
AI-written summary · about
chapters (20)
- 0:00Introduction
- 2:30Containers
- 3:28Terminal window
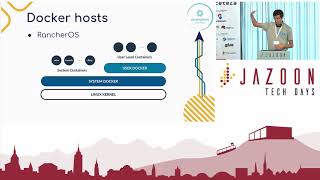
- 5:28Host operating system
- 6:45DrContainers
- 8:18Fork upon
- 11:16Privilege escalation
- 13:28Linux kernel
- 16:53What happens when everything goes fundamentally wrong
- 18:06What happens if an intruder breaks through
- 19:33BasinWay Dr
- 21:21Readonly mode
- 22:14Parma
- 23:08Readonly
- 23:50Docker Secure
- 24:27Dr Hasnat
- 25:21Dr Hasnat signature
- 28:10Docker Registry
- 28:35Dr Pinch
- 32:52Break
related talks
 14mDocker Security
 50mInsights in Container Security
 35mDocker Security
 33mContainers Security Layers and How Not to Break them
 49mVulnerability Exploitation In Docker Container Environments
 43mDocker Security: Start your Container Journey Safely
 33mDocker Security
 32mContainer Security: Exploits, Vulnerabilities and Defense