Don’t be Afraid to Upgrade

summary
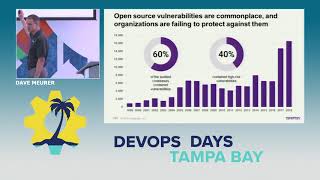
Research of 24,000 open source projects and a 679‑enterprise survey shows concrete wins: top projects release 1.5x more frequently and upgrade dependencies 530x faster (abstract numbers), high‑performing teams deploy 15x faster and remediate vulnerabilities 26x faster, while only 7% remediate within a day and 34% can locate every vulnerable component. Recommends practical controls: generate a software bill of materials, run software composition analysis, surface alerts in IDE/CI, automate dependency updates and use guardrails instead of approval bottlenecks.
AI-written summary · about
chapters (13)
- 0:00Intro
- 2:35Software Supply Chain
- 8:00DevOps Reports
- 9:25Faster is Better
- 13:27Moving Quickly Benefits You
- 17:32Is Faster Better
- 24:35Enterprise Open Source
- 28:04Research Findings
- 29:50The Four Groups
- 31:43The Differences
- 34:58Average Performance
- 37:24Wrapping Up
- 41:22What Did We Find
related talks
 45mDon’t be Afraid to Upgrade
 45mExemplars, Laggards, & The Cautious: A Data-driven Look At High-velocity Software...
 32mExemplars, Laggards, and Hoarders: A Data-driven Look at Open Source Software Supply Chains
 32mAdapting DevOps in a World of Growing Software Supply Chain Attacks
 31m54,000 Tales - A Data-driven Discussion of Exemplar Development and DevSecOps Practices
 25mMaintaining Agility and Security without Impacting Developer Experience
 30mDevSecOps: Understanding Open Source Software risk in your applications
 31mKeep your dependencies in check