The 10 steps of Container Security: It's not that hard !
summary
Concrete checklist: ten essential risk areas are enumerated and mapped to controls using open source Stackrox / Red Hat ACS, with image scanning in CI, signing registries, workload and image policies, and fail the build when necessary via Stackrox CLI. Deploy-time enforcement uses an admission controller or scale-to-zero fallback. Runtime monitoring flags suspicious processes (curl, package managers), enforces behavior baselines, and block pod exec and port-forward to cut lateral movement while guiding a violation remediation process.
AI-written summary · about
chapters (13)
- 0:00Container security challenges
- 1:23Process foundation for security
- 2:27Image vulnerability scanning
- 3:49Secure build process
- 5:57Workload security policies
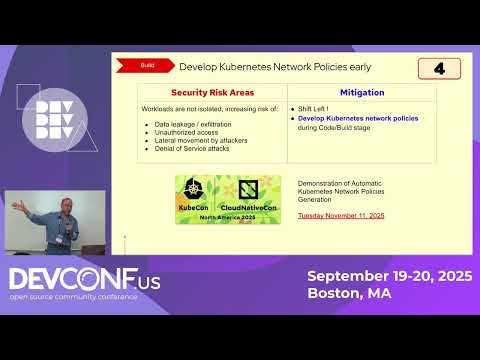
- 7:03Network isolation policies
- 9:51Deploy-time admission control
- 11:14Violation management
- 12:20Runtime attack prevention
- 13:45Monitoring suspicious activity
- 17:39Blocking API calls
- 19:23Protecting Kubernetes resources
- 20:48Q&A
related talks
 24mA Checklist for Security from the Container to the Kubernetes: An Overview End to End
 26mThe 10 Container Security Tricks That (...)
 05mContainer Security Best Practices
- 24mA Checklist for Security from the Container to the Kubernetes: An Overview End to End
 27mContainer Security Best Practices
 32mA Security State Of Mind: Compliance and ...
 48mContainer Security: It’s All About the Supply Chain
 40mSecuring Containers on the High Seas