Data Privacy Engineering to power Responsible Enterprise AI
summary
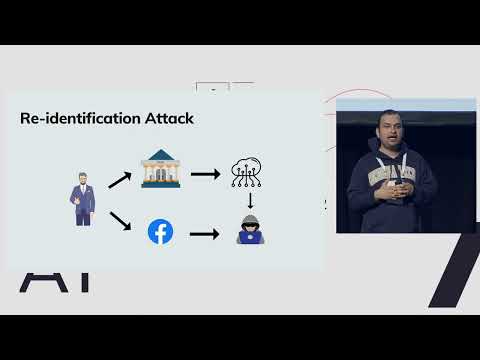
Describes a prototype cloud data exchange and data clean rooms (Snowflake secure UDFs and distributed clean rooms) used for secure joins and multi‑party matching, plus experiments with homomorphic encryption (Microsoft SEAL, IBM HElib using BGV/CKKS), differential privacy tools (PipelineDP, diffprivlib, SmartNoise) with privacy budgets, and AI fairness tooling (AI Fairness 360: ~75 metrics, 10+ mitigations). Shows a re‑identification attack example, test suites and custom validators, a privacy‑score workflow for treatment decisions, and pragmatic Lambda‑style use of treated historical data for near‑real‑time systems.
AI-written summary · about
chapters (19)
- 0:00Intro
- 1:08Data Analytics R&D @ CBA
- 4:15The 2 W's of Data Privacy
- 7:21Re-identification Attack
- 10:45Privacy vs Security Understanding the Difference
- 11:51Responsible Enterprise Al
- 15:02Data Clean Rooms
- 16:06Example: Snowflake Clean Room for Advertising
- 17:13Clean Room Implementations
- 19:12Example: Healthcare Data
- 20:17Homomorphic Encryption Libraries
- 22:17Differential Privacy Example
- 23:50Differential Privacy Libraries
- 25:09Al Fairness & Bias
- 26:17Example: Vicious cycle of Algorithmic Bias
- 27:30Al Fairness Libraries
- 28:34Four Pillars of Privacy Data Engineering
- 29:03Explaining to Stakeholders
- 31:07What's Next in Privacy Space?
related talks
 01h 59mDeep Dive Workshop – Data Security and Data Protection
 28mData Engineers: Privacy Is Your Problem
 26mAnalytics & Data Science with Privacy at its Core
 30mSharing without Sharing: the Case for Data Clean Rooms Powered by Confidential Computing
 15mA Large-Scale Data Clean Room Case Study in Japan
 19mPreserving privacy on data collaboration with AWS Clean Rooms
 29mPrivacy-preserving methods: Building secure projects
 43mPanel: Privacy Design Patterns for AI Systems: Threats and Protections