PerfektBlue: Universal 1-click Exploit to Pwn Automotive Industry…
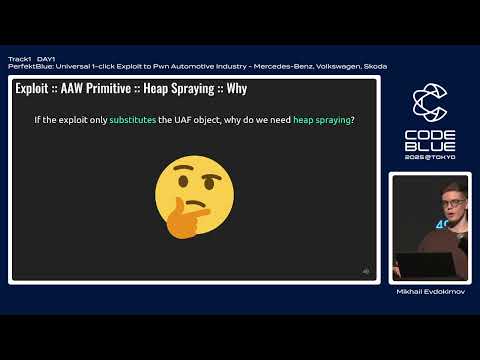
summary
Claim: a chained exploit against BluesDK yields universal one-click remote code execution on millions of IVI units (confirmed on Volkswagen ID4, Skoda, Audi, BMW, Mercedes-Benz). It combines four bugs—an L2CAP remote channel ID flaw, ARFCOM test-response out‑of‑bounds leak, and an AVRCP use‑after‑free plus heap spray—to bypass ASLR/CFI/shadow‑stack, build arbitrary read/write and function call primitives, resolve libc addresses, and spawn a reverse shell; demonstration shows near‑100% stability on the ID4.
AI-written summary · about
chapters (14)
- 0:00Perfect Blue attack overview
- 1:07Bluetooth in automotive infotainment
- 3:14Blues SDK internals
- 8:15Heap spray and UAF
- 16:26Bypassing mitigations with leaks
- 17:07ARFCOM memory leaks
- 21:44L2CAP vulnerabilities
- 26:19Chaining for address leak
- 28:27Arbitrary call and read primitives
- 32:17RCE on Volkswagen ID4
- 34:06Exploitation on other brands
- 37:14Potential impacts and movement
- 38:38Fun facts and timeline
- 39:42Resources and closing
related talks
 51m0-days & Mitigations: Roadways to Exploit and Secure Connected BMW Cars
 34mBack-connect to the Connected Car. Search for Vulnerabilities in the VW Electric Car.
 51mSteering Clear of Danger: Decrypting the Realities of Remote Car Hacking
 37mAutomatic Automotive Hacking
 41mPanel: Tackling Automotive Hardware Vulnerabilities
 40mUnlocking the Drive: Exploiting Tesla Model 3
 18mBluetooth Security Testing with BlueToolkit: a Large-Scale Automotive Case Study
 41mThe (In)Security of Automotive Remote Keyless Entry Systems...