PowerShell obfuskation Techniques & How To Detect Them
summary
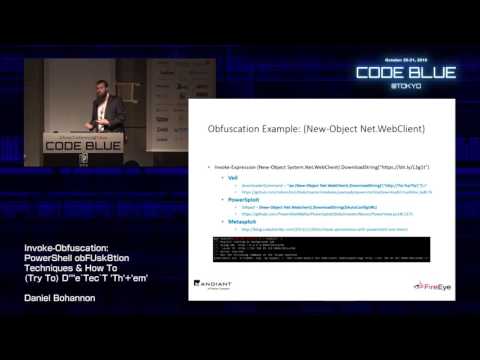
Describes a dozen never-before-seen techniques that mutate PowerShell command arguments so common detections fail, demonstrates concrete methods like tick escapes inside member names, splatting/wildcarded cmdlet names, reversing and reordering string payloads, using securestring as payload to store AES/DPAPI-encrypted scripts, and pushing commands into parent or grandparent processes via environment variables or standard input. Shows evasion of encoded command and remote download cradle detections and ships the open source tool Invoke-Obfuscation which reliably generates and tests these techniques.
AI-written summary · about
chapters (25)
- 0:00Start
- 5:45preparing your environment
- 6:49download a powershell script into memory
- 9:15set new object net web client as a variable
- 10:08add a tick mark
- 10:45put tick marks in front of every letter
- 12:31use tick marks
- 13:55use wildcards to search
- 15:09powershell 10 syntax
- 17:10treat the commandment name as a string
- 21:38automate this in powershell
- 25:16split the string
- 28:40append a wild card to the end of a flag
- 29:20take a random substring
- 31:09convert it to a secure string object
- 31:58using aes encryption 16 24 or 32 bit
- 35:27echo our powershell command into powershell
- 36:50setting your powershell command in a process level environment
- 37:19pipe your command in the clipboard
- 38:41use the clipboard
- 41:44using the remote download cradle
- 44:11randomize the order
- 45:41move the arguments outside of powershell
- 46:36invoke an environment variable
- 47:29push the arguments
related talks
 43mMalicious Payloads vs Deep Visibility: A PowerShell Story
 01h 04mD1T2 - Techniques FOR %F IN (-style) DO (S-level CMD Obfuscation)
 01h 40mDefending against PowerShell attacks - in theory, and in practice
 41mPowerShell Sandbox — Build It Yourself!
 27mUsing PowerShell as a Reverse Engineering Tool
 49mPowerShell for Security Incident Response
 25mInvestigating PowerShell Attacks
 48mStop Writing Insecure PowerShell... Seriously.