Your AI Agent Has Production Access: Now What? (Jack)
summary
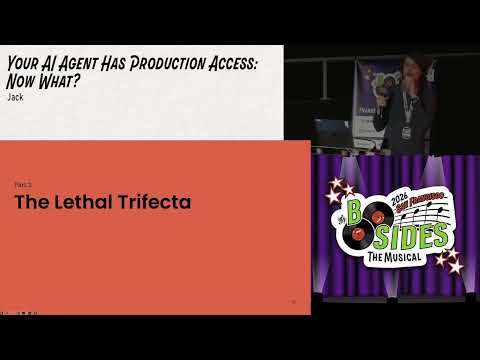
Outlines a practical security stack: identify the lethal trifecta (network egress, sensitive-data access, untrusted input) and remove any leg or severely scope it; run agents inside air‑gapped or sandboxed containers that use short‑lived credentials; replace raw credentials with a tool proxy that enforces repo/branch/file rules and rate limits; record and index full transcripts for postmortem; detect bad behavior with a prompted classifier before or after tool calls and immediately terminate offending agent processes.
AI-written summary · about
chapters (10)
- 0:00Introduction to AI agent risks
- 3:09What is an AI agent
- 5:38Agent threat categories
- 12:08Lethal trifecta of agent risks
- 19:28Surviving executive pressure for agents
- 23:03Sandboxing agents effectively
- 27:12Tool proxies and policy enforcement
- 31:04Detecting misbehaving agents
- 37:18Investigating agent incidents
- 40:27Summary and key takeaways
related talks
 36mHow to Safely Deploy AI Agents that Write and Manage your IaC
 11mBuilding Secure Backend Services with AI Agents
 14mOpenAI on Securing Code-Executing AI Agents
 34mSecure Your Coding Agent Like It’s Malware
 40mIn AI We Trust? Securing the Future, One Agent at a Time
 24mAI Governance for developers: A practical framework for deploying autonomous coding agents safely…
 01h 03mBuilding Secure Infrastructure for Productive AI Agents
 19mKeynote: Towards Building Safe and Secure Agentic AI