Pindemonium: A DBI-Based Generic Unpacker for Windows Executable
summary
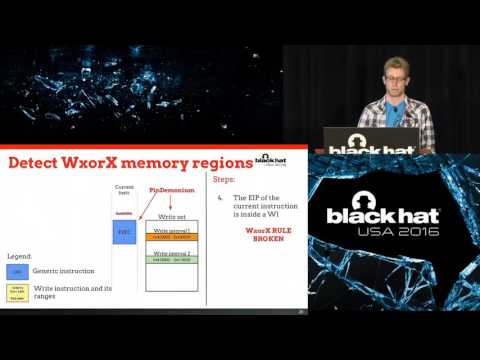
PINdemonium is a DBI-based unpacker built on Intel PIN DBI that detects write-then-execute heap regions, dumps main and heap sections, reconstructs IATs via a plugin system, and produces working PEs. It fully reconstructs 14/17 commercial-packed test binaries and recovers a working unpacked binary for 63% of wild samples, but fails on DBI-evasive packers like Obsidium and incurs ~50x runtime overhead. Source code: https://github.com/Seba0691/PINdemonium
AI-written summary · about
chapters (10)
- 0:00Introduction
- 1:14Malware analysis challenges
- 2:59DBI framework overview
- 4:46Detection and WX rule
- 7:40Memory dumping and reconstruction
- 10:20Advanced features and heuristics
- 13:26Overcoming advanced threats
- 17:36Experimental results
- 20:01System demonstration
- 22:30Q&A session
related talks
 55mHiding PIN's Artifacts to Defeat Evasive Malware
 45mBreak Out of The Truman Show: Active Detection and Escape of Dynamic Binary Instrumentation
 23mAn In-Depth Analysis of Disassembly on Full-Scale x86/x64 Binaries
 24mDefeating the Transparency Feature of DBI
 26mOne Packer to Rule Them All
 40mMalware Reverse Engineering with PE Tree—OSS Inspired by COVID
 26mPANDEMONIUM: Automated Identification of Cryptographic Algorithms
 20mBluePill: Neutralizing Anti-Analysis Behavior in Malware Dissection